Knowledge is Power

Sitewide Search

Search Bare Metal Cyber

Search exact control and technique identifiers, Cyber Wiki articles, framework records, playbooks, books, podcasts, Academy courses, individual lessons, and BMC Cyber Challenge activities.

ISC2 · Free, ad-free audio course

ISC2 CSSLP

A structured, audio-first learning route for ISC2 CSSLP, designed for focused review and practical understanding.

Every Bare Metal Cyber audio course is free and 100% ad-free.

PUT IT INTO PRACTICE

Practice CSSLP concepts

Try 50 original BMC questions, review every explanation, and return to the lessons behind the answer. No login is required. Earn Challenge achievements and share your progress as you go.

50 original questionsExplanation after every answerAchievements and sharing

Independent BMC learning practice—not official exam items, a full mock exam, or an exam-readiness score.

Certification practice in the BMC Cyber Challenge

Companion Books

Study with the audio course, then reinforce it in print.

The study guide helps you organize and revisit the material. The flashcards book adds active recall and rapid review across the course objectives.

Complete Lesson Directory

Choose the exact subject you want to study.

Search by topic or narrow the directory by exam domain. Courses with multiple editions are organized below so every season remains easy to find. Each lesson includes its own audio player, full description, transcript when available, and previous-or-next navigation.

70 lessons available

S01E01Transcript

Getting Started

Confidently Navigate the CSSLP Exam Blueprint

The CSSLP exam blueprint is the definitive source that determines what will be tested, how deeply each topic is covered, and how much each domain contributes to your final score.…

Transcript availableNovember 30, 2025
S01E02Transcript

Getting Started

Demystify Policies, Scoring, and Timing Strategies

Exam policies, scoring rules, and time limits shape how you experience every question on the CSSLP, so understanding them in detail is as important as knowing the domains themselves.…

Transcript availableNovember 30, 2025
S01E03Transcript

Getting Started

Adopt a Practical Audio-Only Study Plan

Preparing for the CSSLP while juggling work and personal responsibilities demands a study plan that fits into the day without sacrificing structure.…

Transcript availableNovember 30, 2025
S01E05Transcript

Domain 1 · Secure Software Concepts

Operationalize Authentication, Authorization, Accounting and Governance

Authentication, authorization, and accounting provide the backbone for identity-aware security in software systems, and governance ensures those mechanisms are defined and enforced in a controlled way.…

Transcript availableNovember 30, 2025
S01E06Transcript

Domain 1 · Secure Software Concepts

Apply Proven Secure Design Principles in Practice

Secure design principles provide a stable foundation for decisions across every CSSLP domain, and many exam questions quietly assume you can recognize and apply them under time pressure.…

Transcript availableNovember 30, 2025
S01E07Transcript

Domain 1 · Secure Software Concepts

Manage Security Within Common SDLC Methodologies

Secure practices must integrate naturally into the software development lifecycle methodologies that organizations actually use, and the CSSLP exam tests your ability to adapt security activities to those different models.…

Transcript availableNovember 30, 2025
S01E08Transcript

Domain 2 · Secure Software Lifecycle Management

Build Security Standards and Organization-Wide Awareness

Consistent security behavior across teams depends on more than individual expertise; it rests on clear standards and a shared understanding of why they matter.…

Transcript availableNovember 30, 2025
S01E09Transcript

Domain 2 · Secure Software Lifecycle Management

Craft a Focused Application Security Strategy and Roadmap

An effective application security strategy gives direction to scattered efforts and provides a framework that exam questions often assume you can interpret.…

Transcript availableNovember 30, 2025
S01E10Transcript

Domain 2 · Secure Software Lifecycle Management

Develop a Complete Security Documentation and Guidance Suite

Security documentation serves as both a control and evidence that controls exist, and the CSSLP exam expects you to recognize the different document types and their purposes.…

Transcript availableNovember 30, 2025
S01E11Transcript

Domain 2 · Secure Software Lifecycle Management

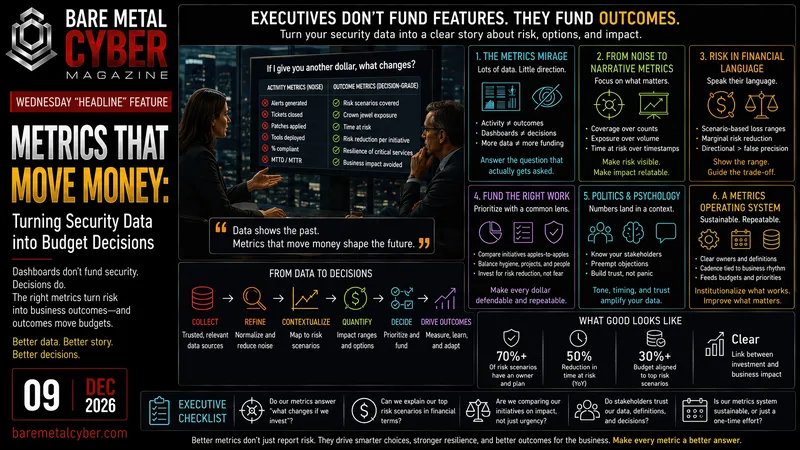
Define Meaningful Security Metrics and Track Outcomes

Security metrics are only useful when they describe reality clearly enough to influence decisions, and the CSSLP exam expects you to distinguish between activity indicators and true outcome measures.…

Transcript availableNovember 30, 2025
S01E12Transcript

Domain 2 · Secure Software Lifecycle Management

Plan Secure, Compliant Application Decommissioning Procedures

Bringing an application to end of life is just as important to security as launching it, and the CSSLP exam reflects this by testing how you handle decommissioning in a controlled, compliant way.…

Transcript availableNovember 30, 2025
S01E13Transcript

Domain 2 · Secure Software Lifecycle Management

Create Clear, Actionable Security Reporting for Stakeholders

Security reporting is the primary way risk, control performance, and emerging issues are communicated to leaders, and CSSLP scenarios often explore whether reporting is truly actionable or just noisy.…

Transcript availableNovember 30, 2025
S01E14Transcript

Domain 2 · Secure Software Lifecycle Management

Integrate Risk Management Methods Into Daily Decisions

Risk management is not only a formal exercise with registers and heat maps; it is also a mindset that should guide everyday decisions, and the CSSLP exam frequently checks whether you can apply that mindset.…

Transcript availableNovember 30, 2025
S01E15Transcript

Domain 2 · Secure Software Lifecycle Management

Implement Reliable Secure Operations Practices End-to-End

Once systems are in production, day-to-day operational practices determine whether security controls remain effective, and CSSLP exam questions regularly examine this operational dimension.…

Transcript availableNovember 30, 2025
S01E16Transcript

Domain 3 · Secure Software Requirements

Define Precise, Testable Software Security Requirements

Clear, testable software security requirements are the bridge between high-level risk statements and the concrete behaviors exam questions expect you to recognize.…

Transcript availableNovember 30, 2025
S01E17Transcript

Domain 3 · Secure Software Requirements

Identify Compliance Obligations Early and Map Controls

Compliance obligations shape many of the decisions covered on the CSSLP exam, from data handling rules to logging expectations and reporting timelines.…

Transcript availableNovember 30, 2025
S01E18Transcript

Domain 3 · Secure Software Requirements

Align Data Classification Requirements With Business Needs

Data classification is a foundational discipline that determines how strongly different information assets must be protected, and CSSLP questions frequently assume you can interpret and apply classification schemes.…

Transcript availableNovember 30, 2025
S01E19Transcript

Domain 3 · Secure Software Requirements

Establish Clear Privacy Requirements and Data Handling Rules

Privacy requirements complement traditional security goals by focusing on how data about people is collected, used, and shared, and the CSSLP exam expects you to handle both perspectives.…

Transcript availableNovember 30, 2025
S01E20Transcript

Domain 3 · Secure Software Requirements

Provision and Govern Data Access Safely and Consistently

Controlling who can see and change data is central to secure software, and the CSSLP exam focuses heavily on whether access is granted and reviewed in a disciplined way.…

Transcript availableNovember 30, 2025
S01E21Transcript

Domain 3 · Secure Software Requirements

Develop Realistic Misuse and Abuse Cases for Resilience

Misuse and abuse cases push you to think like an attacker or a stressed user, and the CSSLP exam regularly checks whether you can anticipate negative behaviors before they appear in production.…

Transcript availableNovember 30, 2025
S01E22Transcript

Domain 3 · Secure Software Requirements

Build Robust Security Requirement Traceability From Start

Traceability is the connective tissue that links risks, requirements, designs, tests, and evidence, and the CSSLP exam expects you to understand how that chain is constructed and maintained.…

Transcript availableNovember 30, 2025
S01E23Transcript

Domain 3 · Secure Software Requirements

Set Enforceable Third-Party and Supplier Security Requirements

Third-party relationships extend your attack surface and regulatory obligations, and the CSSLP exam expects you to treat supplier security as an integral part of the software lifecycle.…

Transcript availableNovember 30, 2025
S01E24Transcript

Domain 3 · Secure Software Requirements

Recap Checkpoint Covering Domains One Through Three

Early CSSLP domains lay the groundwork for how you think about requirements, architecture, and design, and a structured recap helps reinforce those connections before you move deeper into the blueprint.…

Transcript availableNovember 30, 2025
S01E25Transcript

Domain 4 · Secure Software Architecture and Design

Establish Secure Architecture and Foundational Design Choices

Architecture decisions set the long-term security posture of a system, and CSSLP questions often explore whether those decisions create strong or fragile foundations.…

Transcript availableNovember 30, 2025
S01E26Transcript

Domain 4 · Secure Software Architecture and Design

Perform Secure Interface Design for Trustworthy Integrations

Secure interfaces act as contracts between components, teams, and organizations, and the CSSLP exam frequently tests whether those contracts are designed to resist misuse and failure.…

Transcript availableNovember 30, 2025
S01E27Transcript

Domain 4 · Secure Software Architecture and Design

Select Identity and Credential Technologies That Scale

Identity and credential technologies underpin almost every control discussed in the CSSLP, yet many exam scenarios hinge on subtle choices about how those technologies are selected and deployed.…

Transcript availableNovember 30, 2025
S01E28Transcript

Domain 4 · Secure Software Architecture and Design

Apply Virtualization and Trusted Computing to Strengthen Platforms

Virtualization and trusted computing concepts give you tools to isolate workloads, prove platform integrity, and protect secrets, and the CSSLP blueprint expects familiarity with these capabilities.…

Transcript availableNovember 30, 2025
S01E29Transcript

Domain 4 · Secure Software Architecture and Design

Model Threats Effectively Using STRIDE and PASTA

Threat modeling is one of the most powerful analytical tools in the CSSLP toolkit, and structured methods like STRIDE and PASTA help you apply it consistently.…

Transcript availableNovember 30, 2025
S01E30Transcript

Domain 4 · Secure Software Architecture and Design

Evaluate Attack Surface Using Intelligence and Context

Attack surface evaluation tells you where a system is exposed and how attractive those exposures are to real adversaries, and the CSSLP exam expects you to blend technical discovery with contextual understanding.…

Transcript availableNovember 30, 2025
S01E31Transcript

Domain 4 · Secure Software Architecture and Design

Conduct Architectural Risk Assessments That Drive Mitigations

Architectural risk assessments sit at the point where design intent meets real-world threats, and the CSSLP exam expects you to recognize when these assessments are thorough, repeatable, and tied to actual decisions.…

Transcript availableNovember 30, 2025
S01E32Transcript

Domain 4 · Secure Software Architecture and Design

Model Constraints and Operational Architecture for Reality

Systems rarely run in ideal conditions, and the CSSLP exam frequently explores how well designs account for the constraints and operational realities they will face.…

Transcript availableNovember 30, 2025
S01E33Transcript

Domain 4 · Secure Software Architecture and Design

Exam Acronyms: Quick Audio Reference for Learners

Acronyms compress key ideas into a few letters, and the CSSLP exam uses them heavily, expecting you to recall what they stand for and how they relate to secure software lifecycles.…

Transcript availableNovember 30, 2025
S01E34Transcript

Domain 5 · Secure Software Implementation

Apply Secure Coding Fundamentals Across Languages and Stacks

Secure coding fundamentals are language-agnostic habits that reduce entire classes of vulnerabilities, and CSSLP questions routinely distinguish between code that applies these fundamentals and code that does not.…

Transcript availableNovember 30, 2025
S01E35Transcript

Domain 5 · Secure Software Implementation

Sanitize Inputs and Handle Errors Without Leaks

Input sanitization and careful error handling protect systems from both direct exploitation and inadvertent information disclosure, and this combination appears repeatedly across CSSLP domains.…

Transcript availableNovember 30, 2025
S01E36Transcript

Domain 5 · Secure Software Implementation

Analyze Code to Uncover Latent Security Risks

Code analysis is where design assumptions meet implementation reality, and the CSSLP exam expects you to understand how careful review reveals risks that are not obvious from diagrams or requirements alone.…

Transcript availableNovember 30, 2025
S01E37Transcript

Domain 5 · Secure Software Implementation

Implement Application Security Controls That Actually Work

Application security controls only deliver value when they are correctly implemented, consistently enforced, and aligned with realistic use cases, and the CSSLP exam often probes for gaps between intentions and execution.…

Transcript availableNovember 30, 2025
S01E38Transcript

Domain 5 · Secure Software Implementation

Treat Identified Risks and Track Remediation Through Closure

Risk treatment is the process of moving from awareness to action, and CSSLP exam scenarios frequently test whether you can manage that journey in a disciplined, traceable way.…

Transcript availableNovember 30, 2025
S01E39Transcript

Domain 5 · Secure Software Implementation

Integrate Components Safely to Minimize Hidden Couplings

Modern systems depend on many interacting components, and the CSSLP exam emphasizes whether those integrations are designed to limit risk rather than amplify it.…

Transcript availableNovember 30, 2025
S01E40Transcript

Domain 5 · Secure Software Implementation

Secure the Build Pipeline and Protect Artifacts

Build and release pipelines have become prime targets for attackers, and the CSSLP exam increasingly reflects the need to treat them as critical security assets.…

Transcript availableNovember 30, 2025
S01E41Transcript

Domain 6 · Secure Software Testing

Plan a Cohesive Security Testing Strategy Upfront

Security testing is most effective when it grows out of a deliberate strategy rather than a scattered collection of tools and ad hoc activities, and the CSSLP exam tests your ability to recognize that structure.…

Transcript availableNovember 30, 2025
S01E42Transcript

Domain 6 · Secure Software Testing

Design Targeted Attack Surface Test Cases Clearly

Attack surface testing delivers the most value when each test case has a crisp hypothesis about how an exposed element might fail, and the CSSLP exam reflects this focus on precision.…

Transcript availableNovember 30, 2025
S01E43Transcript

Domain 6 · Secure Software Testing

Automate DAST and IAST for Continuous Coverage

Dynamic application security testing and interactive application security testing are powerful when configured and integrated correctly, and CSSLP questions often explore whether they are being used thoughtfully rather than just switched on.…

Transcript availableNovember 30, 2025
S01E44Transcript

Domain 6 · Secure Software Testing

Conduct Penetration and Fuzz Testing With Purpose

Penetration testing and fuzzing provide deep, focused insight into how systems behave under hostile conditions, and the CSSLP exam emphasizes the need for clear objectives and disciplined execution.…

Transcript availableNovember 30, 2025
S01E45Transcript

Domain 6 · Secure Software Testing

Verify Documentation and Uncover Undocumented System Behavior

Documentation is often treated as a static description of a system, yet the CSSLP exam expects you to recognize that written artifacts must be validated against reality.…

Transcript availableNovember 30, 2025
S01E46Transcript

Domain 6 · Secure Software Testing

Analyze Test Results and Track Defects Rigorously

Security testing only creates exam-relevant value when the results are analyzed systematically and defects are tracked from first observation through final closure.…

Transcript availableNovember 30, 2025
S01E47Transcript

Domain 6 · Secure Software Testing

Protect and Govern Security Test Data End-to-End

Security test data presents a unique challenge because it must be rich enough to exercise realistic conditions while still respecting confidentiality, privacy, and regulatory constraints.…

Transcript availableNovember 30, 2025
S01E48Transcript

Domain 6 · Secure Software Testing

Perform Independent Verification and Validation for Assurance

Independent verification and validation provide a higher level of assurance that systems meet their stated requirements and security objectives, and the CSSLP exam expects you to recognize what true independence entails.…

Transcript availableNovember 30, 2025
S01E49Transcript

Domain 6 · Secure Software Testing

Recap Checkpoint: Implementation and Testing Essentials

Implementation and testing domains contain a dense set of practices that influence almost every other part of the CSSLP blueprint, and pausing for a structured recap helps solidify those connections.…

Transcript availableNovember 30, 2025
S01E50Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Perform Operational Risk Analysis to Guide Controls

Operational risk analysis connects live system behavior to the choice and tuning of security controls, and the CSSLP exam frequently evaluates whether that connection is clear.…

Transcript availableNovember 30, 2025
S01E51Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Enforce Secure Configuration Baselines Across Environments

Secure configuration baselines define the minimum hardening level every system must meet, and the CSSLP exam treats them as fundamental controls rather than optional refinements.…

Transcript availableNovember 30, 2025
S01E52Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Release Software Safely Through a Hardened CI/CD

Continuous integration and continuous delivery pipelines determine how changes reach production, and the CSSLP exam increasingly reflects the need to secure those paths end-to-end.…

Transcript availableNovember 30, 2025
S01E53Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Manage Secrets, Keys, and Sensitive Configurations Securely

Secrets management sits at the center of many high-impact breaches, and the CSSLP exam expects a disciplined approach across the entire secret lifecycle.…

Transcript availableNovember 30, 2025
S01E54Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Ensure Secure Installation and Deployment Procedures Consistently

Installation and deployment procedures are moments of high risk, when new systems, configurations, and paths are created, and the CSSLP exam frequently examines whether those moments are controlled.…

Transcript availableNovember 30, 2025
S01E55Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Obtain Authority to Operate Through Evidence and Assurance

Authority to operate represents formal acceptance of risk and confirmation that required controls are in place, and the CSSLP exam views it as the culmination of many lifecycle activities.…

Transcript availableNovember 30, 2025
S01E56Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Monitor Security Using Meaningful, Observable Telemetry

Security telemetry turns raw events into insight about how systems behave, which threats are active, and whether controls are working as intended, and the CSSLP exam expects you to recognize effective monitoring designs.…

Transcript availableNovember 30, 2025
S01E57Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Execute the Incident Response Plan With Confidence

Incident response is where plans and controls are tested under stress, and CSSLP scenarios often examine whether organizations can move from detection to containment and recovery in a structured way.…

Transcript availableNovember 30, 2025
S01E58Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Run Patch Management Effectively Without Business Disruption

Patch management connects vulnerability knowledge to operational change, and the CSSLP exam focuses on whether this connection is timely, prioritized, and controlled.…

Transcript availableNovember 30, 2025
S01E59Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Operate a Measurable Vulnerability Management Program Continually

Vulnerability management goes beyond running scanners; it is a continual process of discovering, assessing, and closing real weaknesses, and the CSSLP exam examines whether that process is balanced and evidence-driven.…

Transcript availableNovember 30, 2025
S01E60Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Integrate Runtime Protection Controls for Live Defenses

Runtime protection adds an active defensive layer while applications are serving real users, and CSSLP questions increasingly probe how these controls fit with design, testing, and operations.…

Transcript availableNovember 30, 2025
S01E61Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Support Business Continuity and Disaster Recovery Objectives

Business continuity and disaster recovery planning connect directly to the CSSLP focus on availability, resiliency, and risk treatment across the software lifecycle.…

Transcript availableNovember 30, 2025
S01E62Transcript

Domain 7 · Secure Software Deployment, Operations and Maintenance

Align Service Levels and SLAs With Security Outcomes

Service levels and formal SLAs influence how software and supporting services are designed, monitored, and improved, and CSSLP items increasingly connect these agreements to security expectations.…

Transcript availableNovember 30, 2025
S01E63Transcript

Domain 8 · Secure Software Supply Chain

Implement Comprehensive Supply Chain Risk Management Practices

Software today depends on a layered supply chain of cloud platforms, third-party services, open-source components, and commercial products, and the CSSLP exam expects you to treat this web of dependencies as a primary risk focus.…

Transcript availableNovember 30, 2025
S01E64Transcript

Domain 8 · Secure Software Supply Chain

Analyze Third-Party Software Security Before Adoption

Choosing a new third-party product or service is effectively choosing to share risk with another organization, and CSSLP questions often examine how thoughtfully that decision is made.…

Transcript availableNovember 30, 2025
S01E65Transcript

Domain 8 · Secure Software Supply Chain

Verify Component Pedigree and Provenance to Reduce Risk

Component pedigree and provenance determine whether you can trust the origins and integrity of the software building blocks in your systems, and the CSSLP blueprint highlights this as a critical element of modern assurance.…

Transcript availableNovember 30, 2025
S01E66Transcript

Domain 8 · Secure Software Supply Chain

Enforce Supplier Security Requirements Through Lifecycle Oversight

Supplier security cannot be assured at contract signing alone; it has to be monitored and enforced throughout the full relationship, which is a recurring theme in CSSLP scenarios.…

Transcript availableNovember 30, 2025
S01E67Transcript

Domain 8 · Secure Software Supply Chain

Support Contracts, Intellectual Property, and Software Escrow

Contracts define how legal, operational, and security responsibilities are shared, and the CSSLP exam often expects you to interpret these agreements from a security and risk perspective.…

Transcript availableNovember 30, 2025
S01E68Transcript

Domain 8 · Secure Software Supply Chain

Recap Checkpoint: Domains Seven and Eight Mastery

Later CSSLP domains extend security thinking into supply chain, operations, and broader governance, and a focused recap helps integrate these topics into a cohesive mental model.…

Transcript availableNovember 30, 2025
S01E69Transcript

Exam Strategy and Review

Crush Exam Day With Calm, Repeatable Tactics

Exam day performance depends as much on process as on knowledge, and CSSLP candidates who manage time, stress, and attention methodically have a clear advantage.…

Transcript availableNovember 30, 2025
S01E70Transcript

Exam Strategy and Review

Essential Terms: Plain-Language Glossary for Fast Review

Key terms and principles appear throughout the CSSLP exam, and being able to recall them quickly in plain language is essential for reading questions correctly and evaluating answer options.…

Transcript availableNovember 30, 2025

A Practical Study Routine

Listen, read, and review in the order that works for you.

01

Listen

Use the free audio course during a commute, walk, workout, or focused study session.

02

Read

Use the study guide to organize the material, annotate key ideas, and build a reference you can return to.

03

Review

Use the flashcards book to practice active recall and quickly revisit weak areas.