
Headline Features
Long-form examinations of significant cybersecurity developments, leadership decisions, and emerging risks.
Listen on Bare Metal Cyber →Bare Metal Cyber Magazine
Read original long-form analysis connecting emerging risks, security leadership, technology, governance, resilience, and practical professional judgment.
Five Magazine Editions
Long-form examinations of significant cybersecurity developments, leadership decisions, and emerging risks.
Listen on Bare Metal Cyber →Practical discussions about cybersecurity work, leadership, careers, risk, and professional development.
Listen on Bare Metal Cyber →A written weekly view of notable developments, recurring themes, and the stories worth carrying into the next week.
Written editionStudy guidance, difficult concepts, certification choices, and focused explanations for learners.
Listen on Mastering Cybersecurity →Focused educational pieces that clarify a concept, framework, technology, or professional challenge.
Listen on Mastering Cybersecurity →Headline Features
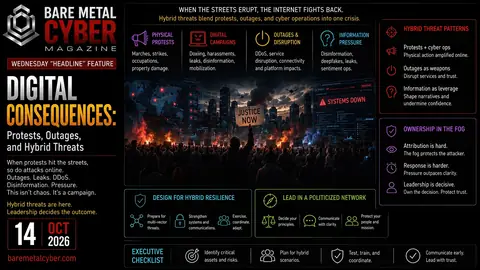
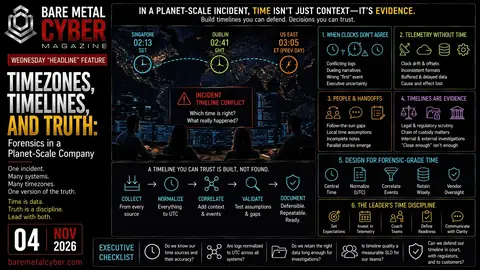
The CISO had three dashboards open and none of them agreed on what was actually happening. Outside, protests were gathering at the company’s headquarters. Inside, a payment API was flapping in and out of service.
Read the feature →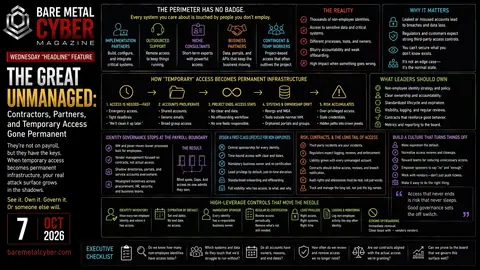
The request looked simple on the change calendar: “Onboard external analytics contractor – temporary access, 90 days.” Six quarters later, the same account is still active in production, tied to a shared mailbox no one really owns, with access to far more than the original scope. No one remembers who approved the extension.
Read the feature →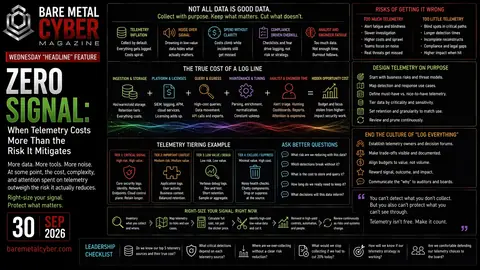
The quarterly renewal meeting starts out like so many others: a slide with last year’s observability and security analytics spend, another with this year’s proposed “optimized” pricing, and a worried finance leader asking why the number keeps going up when incidents keep slipping through. Your teams insist the logs are essential.
Read the feature →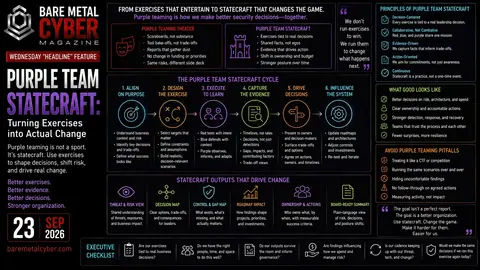
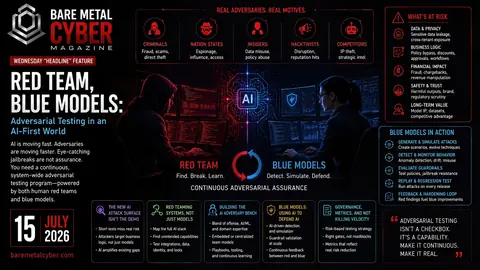
The last purple team exercise “went great” on paper. The red team got in, the blue team caught them, everyone learned a few things, and a dense report landed in a shared drive. Six months later, your incident patterns look the same, your architecture debts are still there, and budget lines have barely moved.
Read the feature →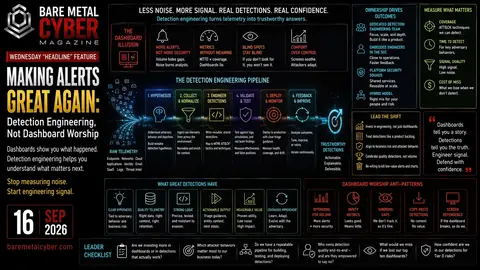
The room is quiet except for the murmur of a dashboard wall. Bars and dials glow in reassuring colors, service names scroll by, and a single, triumphant metric sits at the top: “Alerts processed today: 9,842.” The operations leader is about to brief the CIO, and the plan is simple: point to the screens, talk about volumes and mean time to…
Read the feature →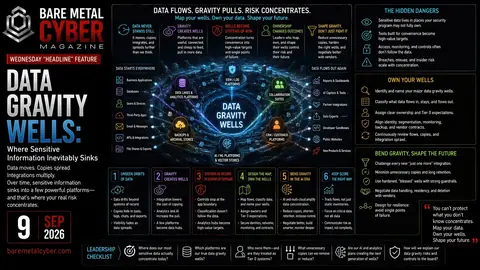
The architecture diagram on the wall looks clean: a few core systems of record in neat boxes, arrows flowing between them, and a tidy ring of controls wrapped around the “crown jewels.” But when you trace how data actually moves in a modern environment, the picture changes.
Read the feature →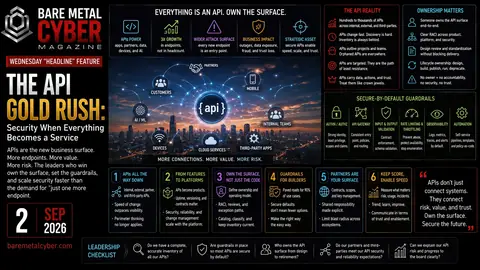
The room is quiet except for the click of keyboards and the hum of the projector. On the wall: a simple chart with one terrifying truth. Your API count has tripled in eighteen months; your headcount, process, and guardrails have not.
Read the feature →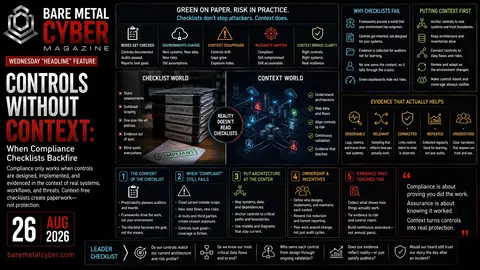
The dashboard says “green.” The annual assessment is done, the latest framework update is accounted for, and the audit committee has the slide they were asking for. But everyone in the room also knows that half the environment now runs on architectures that never existed when those controls were written.
Read the feature →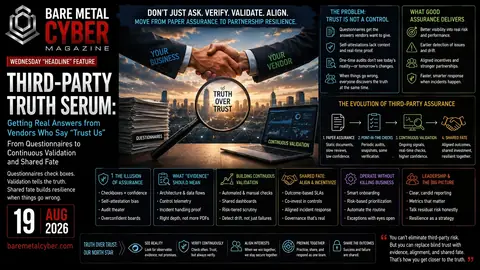
The room is quiet except for the rustle of paper and the hum of a video call on mute. The business wants to sign a new critical SaaS platform, the vendor’s answers to your questionnaire are immaculate, and a glossy report from a well-known audit firm sits on the table.
Read the feature →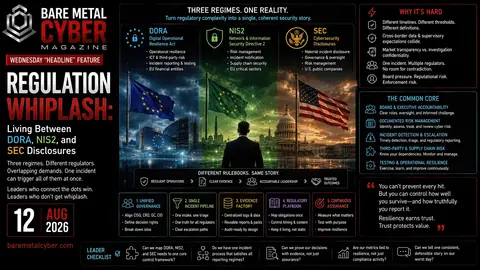
The meeting should have been routine. A major incident has just been contained, and the executive team is reviewing the draft communications plan. Legal wants to hold back until they can pin down “materiality” for the U.S. Securities and Exchange Commission (SEC).
Read the feature →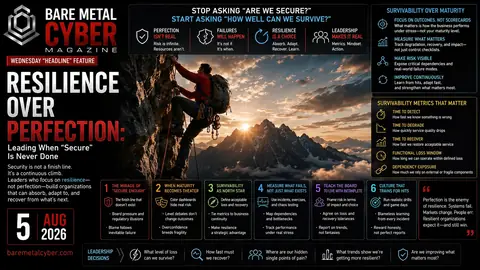
The board chair looks across the table and asks a question you have heard a hundred times in different words: “So… are we secure?” The slide behind you is full of colors, control domains, and maturity scores, but you know none of it can honestly deliver the simple “yes” everyone wants.
Read the feature →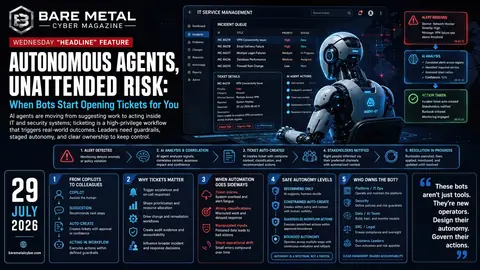
The moment doesn’t look dramatic. Someone proposes flipping a setting so that your AI agent can “helpfully” open tickets on its own instead of just suggesting them in a chat window. A few leaders nod, because tickets feel low stakes compared to pushing code or changing firewall rules.
Read the feature →
Showing 12 of 52 features.